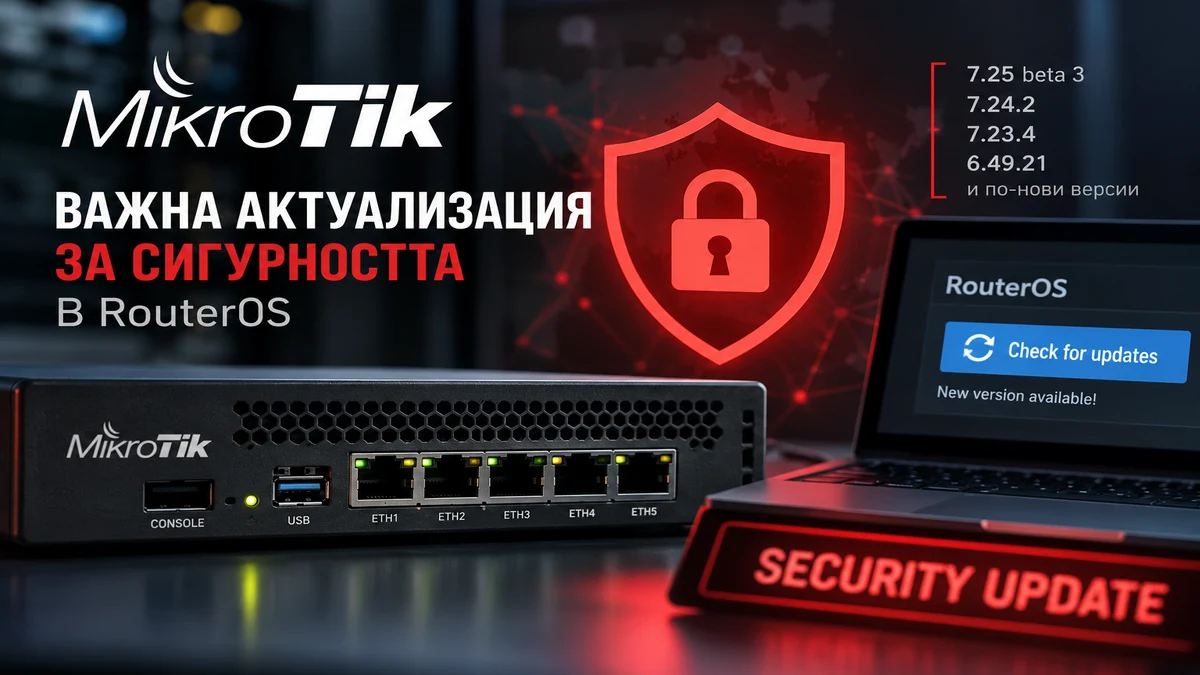
MikroTik has announced that it discovered a security vulnerability in RouterOS and has released patched versions in all update channels.
According to the vendor, this is an important security update. MikroTik states that most configurations are not at risk, but strongly recommends updating. To give users enough time to upgrade their systems, the company is not publishing details about the nature of the vulnerability for now.
The update should already be offered on the device under “Check for updates”.
Versions that include the fix
- 7.25 beta 3
- 7.24.2
- 7.23.4
- 6.49.21
- and all newer versions
According to MikroTik, the issue poses no immediate risk to typical home users and devices running the default configuration. Nevertheless, the vendor recommends that all users update promptly.
Steps after updating
According to MikroTik, after the update RouterOS will check whether the device has been compromised. If a compromise is detected, the device will be placed in the “Flagged” state and the event will be recorded in the Log section.
If the log contains an entry with the critical level stating that the device has received Flagged status, the vendor points to the instructions in the official documentation for that status: Flagged status – MikroTik Manual.
MikroTik also recommends that, even for devices that are not in the Flagged state, the configuration be carefully reviewed after updating RouterOS for:
- unknown scripts;
- unknown users;
- any other settings or configuration that are not recognised.
This review is recommended in all cases, whether or not the device has been flagged. Flagged status does not erase the configuration, so it still needs to be reviewed manually.
At the time of publication, MikroTik had not released further details about the vulnerability.